Table of Contents
Distributed consulting teams often work across several client environments, each with its own systems, accounts, permissions, and security requirements. The same consultant may also work with more than one client with project assignments and access needs changing over time.
Managing that access gets more complicated when teams are distributed. Consultants may connect from different locations and networks while still following the controls set by each client. Access to one client environment also needs to remain separate from access to another.
In this guide, we will walk you through how consulting firms can keep those boundaries clear and give distributed teams the access they need without creating unnecessary exposure across client environments.
Why Secure Client Access Gets Complicated for Distributed Consulting Teams
Several factors make client access harder to manage across a distributed consulting team:
Different Clients Have Different Access Requirements
Clients do not necessarily use the same authentication methods, remote access tools, or network controls. One may require MFA, another may limit access to approved IP addresses, while others may provide their own VPN or remote access platform. Consulting teams need to account for those differences rather than applying the same connection method or access process to every client.
Consultants Often Work Across Multiple Client Accounts
A consultant working with several clients may need separate accounts, permissions, and connection methods for each one. Their colleagues may have a completely different mix depending on the projects they support. As client relationships grow, managing access as a single company-wide permission set becomes less practical. Each consultant’s access needs to match their work for that client.
Project Teams and Access Needs Keep Changing
Consultants join new engagements, move between accounts, cover for colleagues, or take on responsibilities that require different permissions. Their access needs change along with those assignments. Without corresponding changes to permissions, privileges granted for previous work can remain active after they are no longer needed, giving consultants broader reach across client systems than their current role requires.
Client Systems Sit Outside the Consulting Firm’s Control
Consulting firms can manage their own users, devices, and connection methods, but clients control access to their systems. They decide which resources consultants can reach, how users authenticate, and which security requirements apply to external access. A consulting team working across several accounts has to adapt to each client’s controls rather than relying entirely on its own internal access policies.
Related Read: Contractor Lifecycle Management and Access Control in Consulting Firms
Common Security Risks in Multi-Client Access
Working across multiple client environments also introduces security risks that consulting teams need to account for:
Excessive or Outdated Access
Permissions can accumulate as consultants move between projects or take on new responsibilities. Someone who previously needed administrative access for one engagement, for example, could retain those privileges after their role changes. The more unnecessary permissions a consultant holds, the more client resources their account can reach if the credentials are misused or compromised.
Poor Separation Between Client Environments
Client environments need to remain separate even when the same consulting team works across them. Credentials, permissions, or connection methods intended for one client should not provide access to another. Weak separation can increase the impact of a compromised account or incorrectly assigned permission because the exposure is no longer limited to a single client environment.
Inconsistent Access From Distributed Locations
Consultants working from offices, homes, client sites, coworking spaces, or while travelling will not always connect from the same network or public IP address. Changing locations can make client network requirements harder to meet consistently, particularly when access is restricted to approved networks or IP addresses.
Shared Accounts and Credentials
Shared accounts make it difficult to tie activity back to an individual consultant. They also create problems when somebody leaves a project, since changing or removing one person’s access can affect everyone using the same credentials. The risk grows when the same credentials are shared among several people or remain in use after the project team changes.
Access From Untrusted or Uncontrolled Networks
A consulting firm does not control every network its distributed team uses. Consultants working from public or shared networks still need to protect traffic sent to and from client systems. The connection matters even more when the consultant is working with sensitive resources or administrative accounts.
How to Secure Access Across Multiple Client Environments
To manage client access securely, consulting teams can take the following steps:
Keep Client Identities and Credentials Separate
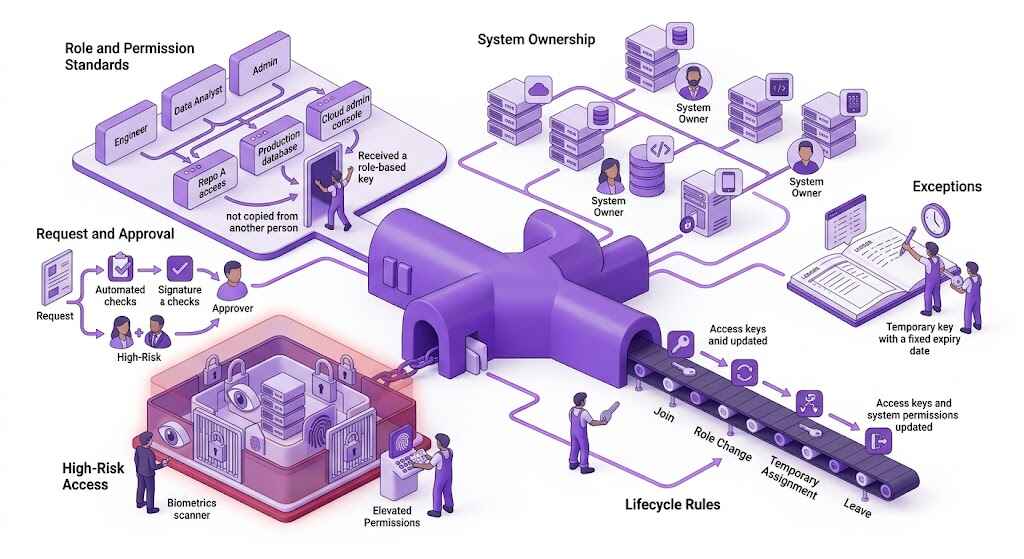
Consultants should use their own accounts for each client rather than sharing credentials with colleagues. Credentials used for one client should also stay separate from those used for another. Doing so makes activity attributable to a specific consultant and allows their permissions to be changed or removed without affecting the rest of the project team.
Apply Least-Privilege Access
Consultants should only have access to the client systems and resources required for their current responsibilities. The same applies to permissions within those systems. A consultant who only needs to review information, for example, does not need administrative privileges simply because other members of the project team have them. Permissions should reflect the work each person performs for that particular client.
Related Read: Implementing the Principle of Least Privilege: A Step-by-Step Guide
Use Strong Authentication
Use MFA and any client-supported identity controls, such as SSO, according to the requirements of each environment. Authentication should remain tied to the individual consultant rather than credentials shared across a project team. Where clients use different authentication requirements, consultants should follow the controls set for each environment rather than treating authentication as a company-wide standard.
Keep Client Access Separate
Access to one client should remain independent from access to another. Client-specific accounts, permissions, network policies, and remote access methods can help maintain that separation. The exact controls will depend on each client’s environment, but authorization for Client A should not create a route into Client B’s systems.
Secure Connections to Client Environments
Consultants may connect to client systems from home, coworking spaces, client sites, or other networks outside the firm’s control. The connection method should follow the client’s requirements while protecting traffic in transit. A business VPN can encrypt traffic between the consultant’s device and the VPN server, while a static IP gives teams a consistent source IP when a client uses IP allowlisting.
Protect Privileged Access
Administrative accounts should be limited to consultants whose work requires elevated permissions. Keeping privileged identities separate from routine accounts also reduces the amount of day-to-day activity performed with administrative rights. Where privileged access management (PAM) is already part of the client’s environment, consultants should follow those controls when using elevated accounts.
Secure the Devices Used for Client Work
Client access also depends on the device making the connection. Consulting firms can set requirements around managed devices, software updates, device encryption, and endpoint protection while meeting any additional controls required by the client. Device requirements add another check beyond whether the consultant has valid credentials for the client environment.
Frequently Asked Questions
Consulting teams can securely work across multiple client environments by using client-specific accounts, least-privilege permissions, strong authentication, and approved connection methods for each environment. Consultants should also follow the security requirements set by each client rather than using the same access arrangement across every account.
The principle of least privilege means giving a consultant only the permissions needed to perform their current work for a client. For example, someone who only needs to review information should not receive administrative privileges. Access should also be updated when the consultant’s responsibilities or project assignments change.
Use separate identities, credentials, permissions, and access methods for each client. An account or authorization intended for one client should not provide a route into another client’s systems. Keeping those boundaries separate can also reduce the exposure created by a compromised account or incorrectly assigned permission.